Skip to the content
CynderHost
  • Status
  • Main Site
  • Client Portal
  • Contact Support
  • Status
  • Main Site
  • Client Portal
  • Contact Support

cPanel

39
  • Getting Started
  • Setting Up And Redirecting To https (SSL)
  • Installing WordPress, Drupal, or Joomla
  • How To Upload And Add Site Files
  • Backing Up cPanel and Websites
  • “SSL Isn’t Working. My Site Shows Not Secure”
  • How To Migrate Your Website From cPanel
  • Export Or Import A MySQL Database With phpMyAdmin
  • Fix “Resource Limit Reached” Errors
  • PHP Workers
  • Change PHP Version in cPanel
  • Enabling GZIP Compression
  • HTTPS Version of URL Is Showing the Wrong Site
  • Adding a Subdomain/Other Domain As a Copy Of a Site (cPanel)
  • Enable Brotli Compression
  • Login To cPanel
  • How to Edit DNS Records in cPanel
  • Adding PHP Extensions (cPanel)
  • Increasing PHP/WordPress Max Upload Size
  • Reinstall WordPress
  • Viewing Hidden (dot) Files in the cPanel File Manager
  • Whitelisting Emails Addresses or Domains from Spam Filter
  • Blacklisting Emails Addresses or Domains from Spam Filter
  • 550 Authentication Required
  • Manage Websites via WP Toolkit
  • Remote MySQL Not Working (Server Connection Error)
  • Cloudflare Not Working When SSL is Set to “Full (Strict)”
  • Restoring a Backup in cPanel
  • Accessing PHPMyAdmin
  • Connecting to and Using FTP
  • Creating a Backup in cPanel
  • Setting Up a Staging Site for WordPress (cPanel/Plesk)
  • Resetting cPanel/Plesk Password
  • Moving/Copying a WordPress Site to a Different Domain in the Same Hosting Plan
  • Add a Subdomain in cPanel
  • Editing PHP.ini Configuration Variables
  • Cloudflare, WordPress, and Redirect Loops
  • Unblocking your IP Address on cPanel
  • Connecting a Cloudflare-Registered Domain

Domain

11
  • Nameservers
  • Adding and Setting Up Domains
  • How To Setup Cloudflare As A CDN
  • How Long Does DNS Propagation Take? Can You Make It Faster?
  • Migrating Your Domain/Website With Zero Downtime
  • Clearing Your DNS Cache (Browsers)
  • Clearing Your DNS Cache (OSes)
  • Previewing Your Website
  • Add a Subdomain in cPanel
  • Connecting a Cloudflare-Registered Domain
  • Setting Up a Domain on High Performance Plans

Plesk

25
  • How To Install WordPress
  • Backing Up Plesk and Websites
  • Export Or Import A MySQL Database With phpMyAdmin
  • Supported PHP Extensions (Plesk)
  • Enabling GZIP Compression
  • How to Edit DNS Records in Plesk
  • Reinstall WordPress
  • FTP Not Working on High-Performance Plans
  • Disabling Caching
  • Unblock an IP From the Firewall
  • Block a URL (Page Rules)
  • Manage Websites via WP Toolkit
  • AWStats/Webstats and Bandwidth Don’t Match Up
  • Contact Form 7 Submission Does Not Work (Loads Forever)
  • Accessing PHPMyAdmin
  • Connecting to and Using FTP
  • Setting Up a Staging Site for WordPress (cPanel/Plesk)
  • Resetting cPanel/Plesk Password
  • Raising the PHP Upload Limit / Max Post Size
  • Moving/Copying a WordPress Site to a Different Domain in the Same Hosting Plan
  • Setting Up DNS Records for Email
  • Adding a New Domain
  • Managing SSL on High Performance Plans
  • Connecting a Cloudflare-Registered Domain
  • Setting Up a Domain on High Performance Plans

WordPress

28
  • How To Speed Up Your WordPress Website
  • Debugging PHP, WordPress, And .htaccess Errors (5XX)
  • Backing Up A WordPress Website
  • How To Migrate A WordPress Website
  • Building Websites With WordPress And Page Builders
  • Using WordPress Plugins
  • WP 5.5 Update Breaks Site
  • Nulled Themes And Premium Plugins
  • Make WordPress Accessible From Multiple Domains
  • Images Not Showing Up After Migration
  • Mixed Content Warnings in WordPress
  • Increasing PHP/WordPress Max Upload Size
  • Reinstall WordPress
  • 404 Errors on WordPress When Accessing Pages, Posts, and Archives
  • Setting Up the CynderHost WordPress Plugin
  • Manage Websites via WP Toolkit
  • Put WordPress in Maintenance Mode
  • Have WordPress Homepage Display a Static Page
  • Disabling WordPress Plugin Without WP Admin Access
  • Locked Out From Website By WordPress Plugin
  • WordPress Security 101: Keeping Your Site Secure
  • Contact Form 7 Submission Does Not Work (Loads Forever)
  • Restoring a Backup in cPanel
  • Accessing PHPMyAdmin
  • Can’t Access WordPress Admin: “Sorry, you are not allowed to access this page.”
  • Setting Up a Staging Site for WordPress (cPanel/Plesk)
  • Raising the PHP Upload Limit / Max Post Size
  • Moving/Copying a WordPress Site to a Different Domain in the Same Hosting Plan

Web Development

7
  • How To Create A Hello World Website
  • Debugging PHP, WordPress, And .htaccess Errors (5XX)
  • Changing Your Hosts File
  • Clearing Your DNS Cache (Browsers)
  • Clearing Your DNS Cache (OSes)
  • Previewing Your Website
  • Setting Up a Staging Site for WordPress (cPanel/Plesk)

Client & Billing

14
  • Contacting Support
  • Site/Service Has Been Suspended or Terminated
  • Overdue And Recurring Invoices
  • Can’t Verify My Email Address
  • How To Cancel a Subscription
  • Invoice Payment Isn’t Showing Up
  • Can’t Sign In With Google
  • Pay an Invoice
  • Email Verification Isn’t Working
  • Setting Up a Stripe/CC Recurring Payment
  • Setting Up a Recurring PayPal Subscription
  • Resetting cPanel/Plesk Password
  • How to Upgrade or Downgrade a Plan
  • Check Remaining Funds/Balance

NitroPay

6
  • What Is NitroPay?
  • Signing Up For NitroPay
  • NitroPay Payments
  • How To Add Ads To Your Site
  • Setting Up Your Ads.txt
  • Ad Placement Tips for Best Earnings

API

3
  • Cache API Reference
  • Setting Up the CynderHost WordPress Plugin
  • CynderHost High Performance API Key

Emails

12
  • How to Adjust Spam Filters?
  • Incoming Emails Going to Spam?
  • Whitelisting Emails Addresses or Domains from Spam Filter
  • Blacklisting Emails Addresses or Domains from Spam Filter
  • 550 Authentication Required
  • Microsoft Office 365 / Hotmail / Gmail Delivering My Emails to Spam
  • Email Rejected By Gateway
  • Setting Up DNS Records for Email
  • Adding a New Domain
  • Logging into the Email Panel
  • Creating an Email Account
  • Checking Email via Webmail, and IMAP/POP3
View Categories

WordPress Security 101: Keeping Your Site Secure

6 min read

0:00 / 6:34
  • View as Markdown Open this page as plain Markdown (opens in a new tab)
  • Open in ChatGPT Ask questions about this page (opens in a new tab)
  • Open in Claude Ask questions about this page (opens in a new tab)
  • Open in Google AI Studio Ask questions about this page (Google account required) (opens in a new tab)

Proper WordPress security requires a two-pronged approach. Secure servers used for hosting, and proper application-side security.

At CynderHost we take care of the former, through filesystem isolation, security scans, and audits, vulnerability scanning, and protection against various attacks (especially for our high-performance users).

You, the webmaster/site owner also play an essential role in WordPress security though. You’re responsible for keeping your application secure, which is what we’ll be covering here.

Without one of these, your site isn’t secure, and you could be easily hacked or infected with malware.

Passwords #

Strongs passwords are arguably the most integral part of securing your site. Not having a strong password is equivalent to using the same key to lock your house as your entire neighborhood. Attackers and automated bots very frequently attempt to brute for your WP Admin administrator account with common password combinations.

While brute force protection helps prevent compromise, it’s ultimately not effective if your password isn’t strong, as attacks have hundreds of thousands of devices they can cycle through. As a rule of thumb, passwords should be 12 characters or more at a minimum and contain a special character, capital letter, lower case letter, and numbers. We recommend 16+ character passwords.

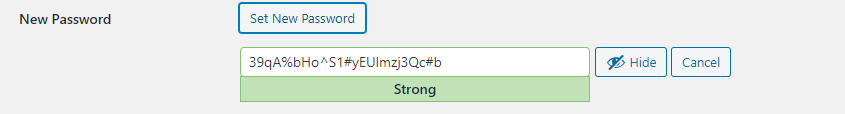
If you have trouble coming up with a password, we recommend utilizing WP’s built-in password generator with a secure third-party password manager.
Dual Factor Authentication #

If your password were to be leaked, it doesn’t matter how strong it is, malicious actors would have access to your site.

To help prevent this, we also recommend implementing 2FA for your WP Admin. You can utilize a plugin such as Loginizer or WordFence to have an OTP (one-time passcode) sent to a device you control when you try to log in.

Nulled Themes and Plugins #

Don’t use them. Period. We cover more here.

Plugin/Theme/Core Updates #

Keeping your files, plugins, themes, and WP core up to date is another essential part of proper WP security. Outdated plugins lack the proper security patches, may have vulnerabilities, and may no longer be supported by plugin authors.

When in doubt, turn on minor core, plugin, and theme auto-updates so you can keep your sites up to date.

WAF #

(A web application firewall…not waffles)

A WAF is a firewall that sits between your visitors (the end-user) and your site. It intercepts all requests and scans them for potentially malicious actions. This could include zero-day exploits, SQL injections, XSS attacks, and more.

Utilizing a WAF will impact your site’s performance. In most cases though, the tradeoff isn’t big, and keeping your site secure is more important. Here’s more on how a WAF works.

There are many different vendors to choose from. We recommend WordFence (the plugin) as a WordPress-side WAF, and Cloudflare, Incapsula, or Sucuri as a cloud-based WAF. Using two is usually redundant and not needed, as long as the one you are using provides aquedate protection.

Keep in mind, no WAF is 100% accurate. You’ll likely deal with false-positives (which you can whitelist) – and false negatives (where the WAF doesn’t detect a malicious request). Therefore, the other parts of WP security are still extremely important.

Note: High-Performance hosting users have a WAF built-in. As such, an external/third-party WAF is not recommended.

PHP Versions #

You may not believe it, but many WordPress sites still run on PHP 5.6…or earlier. These versions are no longer maintained (End of Life) and riddled with security issues. If you’re not on a supported PHP version (see: https://www.php.net/supported-versions.php) then upgrade as soon as possible. Just take a backup before you do.

Security Audits #

Even if you follow all the guidelines above, your site may still be hacked. Why? Zero-day vulnerabilities that have not been discovered by security researchers may exist in the wild, actively being exploited.

Knowing you’ve been hacked is the first step to recovery. Run monthly, or weekly scans of all your files to ensure they are clean and free of malware. We recommend using WordFence for our shared hosting users. High-Performance customers have their sites automatically scanned periodically, server-side – and can run a security audit directly from the panel.

Backups #

Uh-oh! So you’ve been hacked. Now what?

While you could go through the tedious process of cleaning your site manually or paying someone to do this, we generally recommend:

  1. Backing up the current state of your site
  2. Restoring to a previous backup
  3. Scanning, and verifying the site is clean
  4. Figuring out/patching any attack vectors
  5. Monitoring closely for more attacks/exploits

Of course, this is contingent on you having backups. We keep automated, daily (at minimum) backups of your site you can restore to. That said, it is highly recommended that you keep your own backups. This can be done through a plugin like WP Vivid Backup & Restore, Akeeba Backup and Restore, or Updraft.

If you find your site is hacked, please reach out to our support team. We may be able to clean it up for you.

Minor Tweaks, and Advanced Security #

If you know what you’re doing, proceed. Otherwise, contact us or skip this section.

Disallowing PHP Execution in wp-content/uploads #

Many exploits rely on improper file-upload sanitization in order to upload PHP scripts and execute them. Preventing these uploads and execution can help prevent backdoors or further attack vectors. A plugin like WordFence can do this for you, as well as our high-performance panel (“Check Security” -> “Forbid execution of PHP scripts in the wp-content/uploads directory(can be reverted)”)

Preventing WordPress Filesystem Modification #

Danger: This could break your site.

You can prevent anyone, including yourself, from modifying WordPress core, plugin, and theme files. This prevents attackers from injecting malicious code into WP Core, as exploits commonly do.

This will also break WP Core updates, plugin and theme updates, and any other feature that modifies WP Core.

Please take a backup before doing this.

To lockdown, your filesystem, select all the files (not folders) and change the permissions to r–r–r– (read-only/444). Folders should have r-xr-xr-x permissions (0555). Exclude the wp-content/uploads folder from this, as you need to be able to write to that folder in order to upload media files.

If you’re on your own server, you can chattr +i all your files to prevent chmod() calls from changing permissions. This is not recommended.

Disable XMLRPC.php #

If you don’t need it, XMLRPC can be disabled to reduce attack surface. To disable XMLRPC, you can add the following to your functions.php

// Disable use XML-RPC
add_filter( 'xmlrpc_enabled', '__return_false' );

// Disable X-Pingback to header
add_filter( 'wp_headers', 'disable_x_pingback' );
function disable_x_pingback( $headers ) {
    unset( $headers['X-Pingback'] );

return $headers;
}

Or this to your .htaccess:

<Files xmlrpc.php>
order allow,deny
deny from all
</Files>

If all of this is way over your head, just contact us.

Updated on November 26, 2021

What are your Feelings

  • Happy
  • Normal
  • Sad

Share This Article :

  • Facebook
  • X
  • LinkedIn
  • Pinterest
Locked Out From Website By WordPress PluginContact Form 7 Submission Does Not Work (Loads Forever)
Table of Contents
  • Passwords
  • Dual Factor Authentication
  • Nulled Themes and Plugins
  • Plugin/Theme/Core Updates
  • WAF
  • PHP Versions
  • Security Audits
  • Backups
  • Minor Tweaks, and Advanced Security
  • Disallowing PHP Execution in wp-content/uploads
  • Preventing WordPress Filesystem Modification
  • Disable XMLRPC.php

© 2026 CynderHost

Powered by WordPress

To the top ↑ Up ↑